AI is moving from experimentation to enterprise strategy. But as organizations embed AI into operations, customer experiences, decision-making, and business processes, one question should come before “How quickly can we adopt AI?”
“How securely can we adopt it?”
The organizations that gain the most from AI will not necessarily be those that adopt it the fastest.
They will be the ones that can scale AI responsibly, securely, and with confidence.
Why AI Security Should Be a Priority
AI introduces a new layer of complexity into an organization's technology environment.
Enterprise AI systems may interact with:
Customer and employee data
Financial information
Intellectual property
Internal applications
Cloud environments
Enterprise databases
APIs and third-party platforms
Business-critical workflows
This means a security weakness in an AI implementation can potentially extend beyond the AI application itself and affect the wider enterprise.
Can our organization control the data, access, applications, infrastructure, and processes surrounding AI?
That is the foundation of secure AI adoption.
The AI Opportunity Comes With a New Risk Landscape
Organizations are adopting AI for everything from customer service and employee productivity to analytics, automation, software development, and decision support.
But AI can introduce risks that traditional cybersecurity strategies may not fully address.
Some of the key areas include:
1. Sensitive Data Exposure
Employees and applications may unintentionally expose confidential information when using AI tools.
Organizations need clear policies and technical controls around what data can be accessed, processed, stored, or shared through AI systems.
2. Identity and Access Risks
As AI becomes integrated with enterprise applications, determining who or what is allowed to access specific data and systems becomes increasingly important.
Strong identity, authentication, authorization, and access controls are essential.
3. Third-Party and AI Supply Chain Risk
Enterprise AI rarely operates in isolation.
Organizations may rely on cloud providers, AI models, SaaS platforms, APIs, data providers, and technology partners.
Each additional dependency can introduce another potential security and compliance consideration.
4. Model and Application Security
AI applications themselves need to be secured.
Organizations should consider risks such as unauthorized access, malicious inputs, data leakage, insecure integrations, and weaknesses in the applications surrounding AI models.
5. Governance and Compliance
As AI adoption grows, businesses need to understand how AI systems are being used, what information they process, who has access, and whether their usage aligns with internal policies and applicable regulatory requirements.
AI Security Is Bigger Than Protecting the AI Model
One common mistake is to treat AI security as a standalone technical problem.
In reality, enterprise AI security sits across multiple layers of the technology ecosystem.
A secure AI strategy should consider:
If one of these layers is poorly controlled, the overall AI environment can become vulnerable.
This is why AI adoption should be connected to the organization's broader cybersecurity, cloud, data, identity, and digital transformation strategy.
Five Questions Should Ask Before Scaling AI
Before moving from AI pilots to enterprise-wide adoption, leadership teams should be able to answer five questions.
1. What data will our AI systems access?
Not all enterprise data should be treated equally.
Leadership should understand:
What information is being used?
Where is it stored?
Who can access it?
Is it sensitive or confidential?
Where is it processed?
Are third-party AI platforms involved?
Without data visibility, it becomes difficult to manage AI risk effectively.
2. Who can access our AI systems?
AI adoption creates another reason to strengthen enterprise identity and access management.
Organizations should establish appropriate controls around:
User authentication
Multi-factor authentication
Role-based access
Privileged access
Application identities
API access
Third-party access
The objective is simple:
The right user or system should have the right access to the right resource at the right time.
3. What happens if an AI system is compromised?
AI should be treated as part of the enterprise attack surface.
Leadership should understand how the organization would detect, investigate, contain, and recover from a security incident involving an AI application or its connected systems.
This requires more than prevention.
It requires continuous monitoring, threat detection, incident response, and resilience.
4. Can we monitor AI-related activity?
You cannot effectively manage a risk you cannot see.
Organizations should establish visibility across relevant:
Applications
Users
Devices
Cloud environments
APIs
Data flows
AI services
Security events
Security monitoring and analytics can help organizations identify unusual activity and respond to potential threats faster.
5. Who owns AI security?
AI security should not belong exclusively to the IT or cybersecurity team.
A successful enterprise AI strategy requires collaboration between:
Business leadership + IT + Cybersecurity + Data + Legal/Compliance + Risk
The CEO's role is particularly important in establishing accountability and ensuring that AI adoption supports business objectives without creating unmanaged enterprise risk.
From AI Experimentation to Secure Enterprise Adoption
Many organizations begin their AI journey with individual pilots.
That is useful for experimentation but scaling AI requires a different mindset.
A pilot might involve one team, one application, and limited data.
Enterprise AI could involve:
Multiple business units
Multiple AI applications
Large datasets
Cloud platforms
Enterprise applications
Customer-facing systems
Automated workflows
Third-party technology providers
The security strategy therefore needs to evolve as AI adoption grows.
For organizations working within the Oracle ecosystem, Oracle AI and analytics capabilities can also form part of a broader enterprise data and AI strategy.
Cybersecurity and AI Should Be Designed Together
AI should not be something the cybersecurity team is asked to secure after the technology has already been deployed.
Security should be considered from the beginning of the AI lifecycle.
This means evaluating security during:
Strategy → Architecture → Development → Integration → Deployment → Operations
This approach can help organizations avoid the costly process of retrofitting security after an AI solution has already become embedded in business operations.
Security is not simply a cost associated with technology.
It becomes an enabler of responsible innovation.
Building an Enterprise Security Foundation for AI
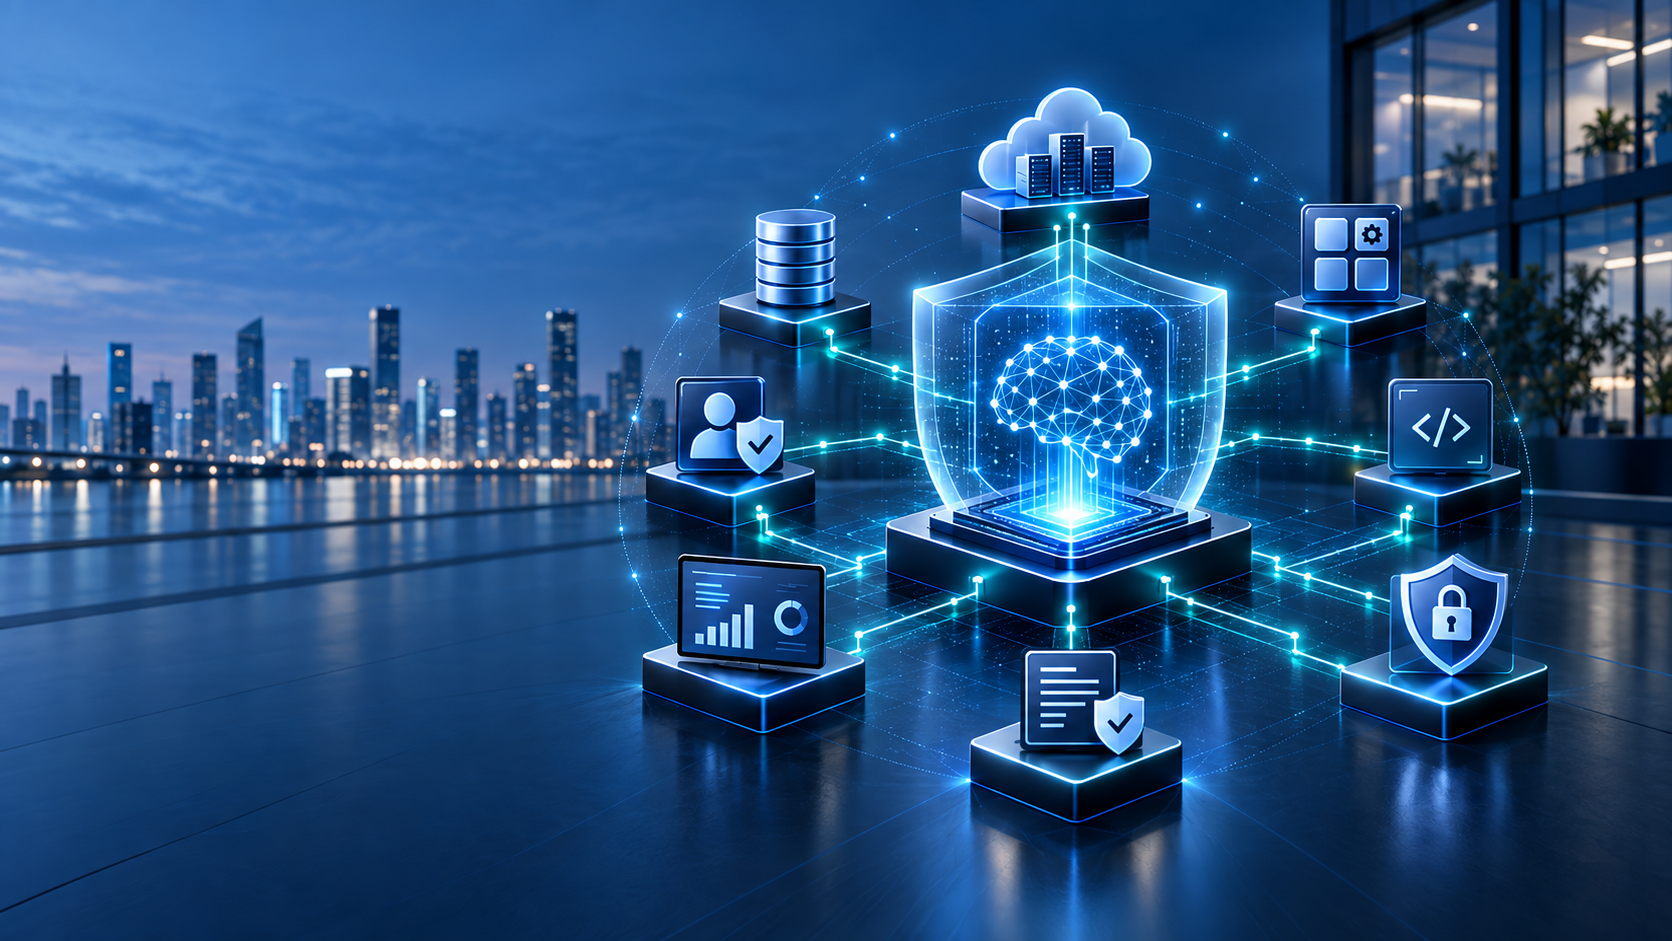
A strong AI security foundation typically brings together several capabilities.
Identity & Access Management
Control who can access AI applications, data, platforms, and connected enterprise systems.
Cloud Security
Protect the cloud infrastructure, workloads, configurations, identities, and data supporting AI environments.
Application & API Security
Secure the applications and APIs through which AI systems interact with users and enterprise platforms.
Data Security
Protect sensitive information throughout its lifecycle and establish appropriate controls around AI data usage.
Security Monitoring
Improve visibility into activity across users, applications, infrastructure, and security environments.
Threat Detection & Incident Response
Identify suspicious activity and establish processes for investigation, containment, and recovery.
Governance & Risk Management
Create policies, controls, accountability, and oversight for responsible AI adoption.
Together, these capabilities create a security foundation that allows organizations to adopt AI without treating security as an afterthought.
The Business Case for Secure AI Adoption
For CEOs, cybersecurity investment needs to connect to business outcomes.
A secure AI strategy can help organizations:
Protect Customer Trust
A security incident involving customer or confidential data can have consequences far beyond the immediate technical impact.
Reduce Business Disruption
Strong prevention, detection, and response capabilities can improve organizational resilience.
Accelerate Responsible Innovation
When security and governance are built into the AI strategy, business teams can adopt new technologies with greater confidence.
Improve Risk Visibility
Leadership gains a clearer understanding of where AI-related risks exist across the organization.
Support Scalable Transformation
A repeatable security foundation makes it easier to expand AI initiatives across departments and business functions.
What you Should Take Away
AI adoption is no longer a question of whether organizations will use AI.
The more important question is:
Can your organization scale AI without creating unacceptable security and business risk?
The answer depends on the foundation beneath the technology.
Organizations need to think beyond the AI model itself and consider the broader ecosystem of data, identity, applications, APIs, cloud infrastructure, cybersecurity, monitoring, governance, and people.
The organizations that build this foundation early will be better positioned to move from isolated AI experiments to secure, enterprise-wide AI adoption.
Is Your Organization Ready for Secure AI Adoption?
Before scaling your next AI initiative, evaluate your organization's security readiness across identity, data, applications, cloud, infrastructure, monitoring, and governance.
DWT Technology helps enterprises navigate complex technology environments across cybersecurity, cloud, enterprise applications, data, analytics, AI, and digital transformation.
Our specialists can help you identify security considerations across your technology environment and build a practical roadmap for more secure AI adoption.
Building an enterprise AI strategy? Start by understanding your security readiness. Speak with DWT Technology's enterprise technology and cybersecurity specialists.